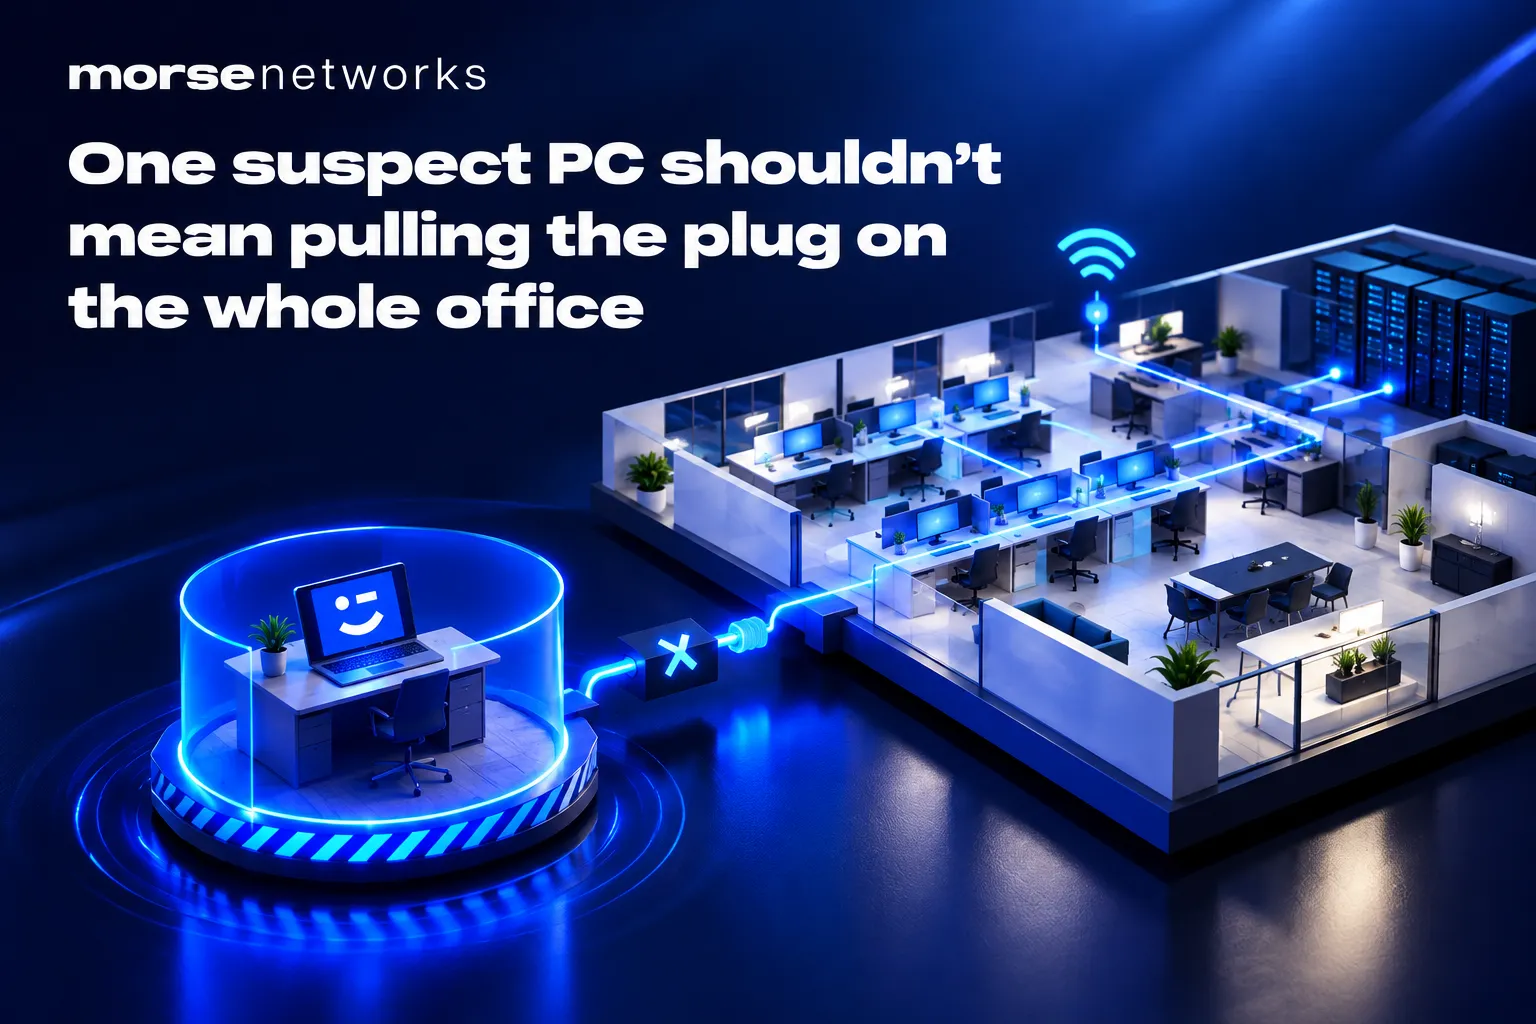
Someone spots something odd on their PC. Files won’t open, a warning appears, or the mouse seems to have developed ambitions of its own.
They shout for help. A colleague heads towards the router.
That’s a good moment to have a plan.
If a computer might be compromised, your team should know how to disconnect that machine from the network and report it. Switching off the office internet in a panic can disrupt everyone while leaving the suspect computer connected to other devices locally.
For business owners, this makes network isolation a useful thing to practise before anyone needs it.
Know what you’re disconnecting
A PC can have more than one network connection. Pulling out its Ethernet cable won’t isolate it if it automatically switches to Wi-Fi. Turning off Wi-Fi won’t help if it’s still plugged into a network socket.
Start by making devices easy to identify. Give each business computer a clear asset label and record who uses it. Your IT team should be able to match that label to the device in their management tools.
“Sarah’s laptop, asset MN-024” is useful. “The silver one near accounts” leaves rather more room for interpretation.
Staff also need to recognise the network cable and know where their Wi-Fi controls are. That sounds basic until someone is trying to find them with a worrying message covering the screen.
Disconnect the machine, not everyone’s working day
For an ordinary office PC, a staff isolation procedure will usually involve unplugging its Ethernet cable and switching off Wi-Fi. Any other active network connection, such as mobile data, needs to be considered too.
Your IT team should confirm the exact steps for your devices. Keep those instructions somewhere staff can reach without using the affected computer.
Where suitable security tools are installed and configured, IT may also be able to isolate a device remotely. Agree who can authorise that action and how urgent requests reach them.
Staff shouldn’t start unplugging switches, access points or routers unless the incident lead tells them to. Those boxes may support phones, payment systems and other people’s work.
There are situations where wider isolation is necessary. That should be a deliberate decision made by someone who understands the network.
Agree what happens about power
Disconnecting a computer and shutting it down are different actions. Your incident procedure needs to explain both.
Turning off a machine can remove information held in its memory that may help an investigation. Leaving a compromised machine running can also carry risks, particularly if destructive activity continues after it loses its network connection.
There isn’t one power-off rule that fits every incident. Ask your IT provider or security lead to set a clear policy, including what staff should do when they can’t reach anyone immediately.
Once a device has been isolated, staff should avoid restarting it, running their own clean-up tools or reconnecting it to see whether it’s better. A quiet screen doesn’t prove the problem has gone away.
Give people one clear reporting route
A reporting process should work when the affected PC doesn’t.
If your instructions live only in email or a shared folder, staff may lose access at exactly the wrong moment. Keep an accessible phone number and an alternative contact route, with clear arrangements for out-of-hours incidents.
Ask staff to report the device label, what they noticed and when it happened. They should also explain which connections they’ve disconnected and whether they’ve switched the machine off.
A photograph of an on-screen warning may help, if your policy allows it and sensitive information is handled appropriately. Nobody should delay reporting while trying to produce a beautifully formatted incident report.
Make the tone clear too. Someone who reports a suspicious attachment promptly has given the business a chance to act. Turning the moment into a public cross-examination is unlikely to improve the next report.
Check whether your network supports containment
Disconnecting one PC is easier when the network is understood and documented.
Your IT team should know which equipment serves each area, how office Wi-Fi is managed and which devices can communicate with one another. They should also be able to identify a particular computer without relying entirely on the person sitting in front of it.
Separating guest Wi-Fi from business systems is a sensible starting point. Other separation may be appropriate for payment equipment, building controls or business-critical systems, depending on the risks and how those services work.
Network separation can limit the routes available to an attacker. It needs careful configuration and testing, rather than confidence in a Wi-Fi network name containing the word “Guest”.
Also check what happens when the internet connection goes down. Devices on the same local network may still be able to communicate. Pulling the router’s broadband cable doesn’t necessarily isolate a suspect PC from the office.
Rehearse it without causing an actual outage
Start with a short discussion around a hypothetical incident. Choose an ordinary workstation and describe a suspicious warning appearing during the working day.
Ask the person using it to explain how they would identify the device, disconnect it and contact the right person. Have your IT contact confirm the steps.
Keep the first exercise verbal. If you later test physical disconnection, arrange it with IT and the device’s user so you don’t interrupt live work or critical equipment.
Include a laptop that uses both wired networking and Wi-Fi. Check what a remote worker would do as well, especially if their usual way of contacting support depends on the affected machine.
Write down anything unclear and fix the instructions. The exercise has done its job if it exposes confusion while everyone’s afternoon is still intact.
Make the first response straightforward
Your staff don’t need to diagnose malware. They need a safe, agreed way to recognise a concern, isolate the right device and get help.
Choose a workstation this week and walk through that process with your IT contact. Check that the instructions match the equipment people actually use, then make sure the reporting number is easy to find.
If the chat with your IT guys make your spidey senses tingle and you’d like another chat about your office network and incident-containment arrangements, get in touch with us at Morse Networks urgently.
Let’s make IT one less thing to think about. morsenetworks.co.uk.